A 24/7 SOC and SIEM fabric around every tenant
Enterprise and operational systems report into one correlation engine, watched continuously by L1–L3 analysts. Containment, forensics and the audit pack that regulators ask for are produced from the same evidence stream.
24/7
L1–L3 analyst coverage
IT + OT
One correlation engine
Zero Trust
Architecture baseline
5
Phase maturity roadmap
The four-layer security fabric
Each layer has a defined responsibility and a defined output. Together they turn scattered alerts into a single operational narrative.
Layer 01 · Ingestion
Enterprise & operational systems
Endpoints, cloud applications, firewalls, servers, ERP/CRM, SCADA, OT PLCs and industrial IoT controllers.
Layer 02 · Intelligence
Central SIEM platform
Event collection, a correlation engine, behavioural anomaly analytics and automated alert routing.
Layer 03 · Operations
24/7 SOC operations centre
Continuous monitoring, proactive threat hunting, incident triage, containment and forensic response.
Layer 04 · Assurance
Governance, audit & compliance
NERC-CIP, IEC 62443 and ISO 27001 regulatory audits, board risk dashboards and resilience metrics.
Five-phase SOC/SIEM maturity roadmap
The journey from unknown exposure to automated defence. Select a phase to see what changes.
Assessment & discovery
Full asset mapping and gap audit across IT and OT estates. We establish what actually exists, what is internet-reachable, what is unpatched and which industrial controllers have no monitoring at all.
- Asset and network topology discovery
- Control gap audit against IEC 62443
- Risk-ranked remediation backlog
What the SOC actually does at 03:00
An operations centre is only as good as its procedures. Triage, authority and evidence handling are written down, rehearsed and reviewed.
Triage & validation
Alert validation, context enrichment and false-positive suppression before escalation.
Investigation & containment
Scope determination, host or segment isolation and coordinated recovery with operations.
Threat hunting & forensics
Hypothesis-driven hunting across the estate and root-cause forensics on confirmed incidents.
Automated response
Repeatable containment steps automated so analysts spend time on judgement, not keystrokes.
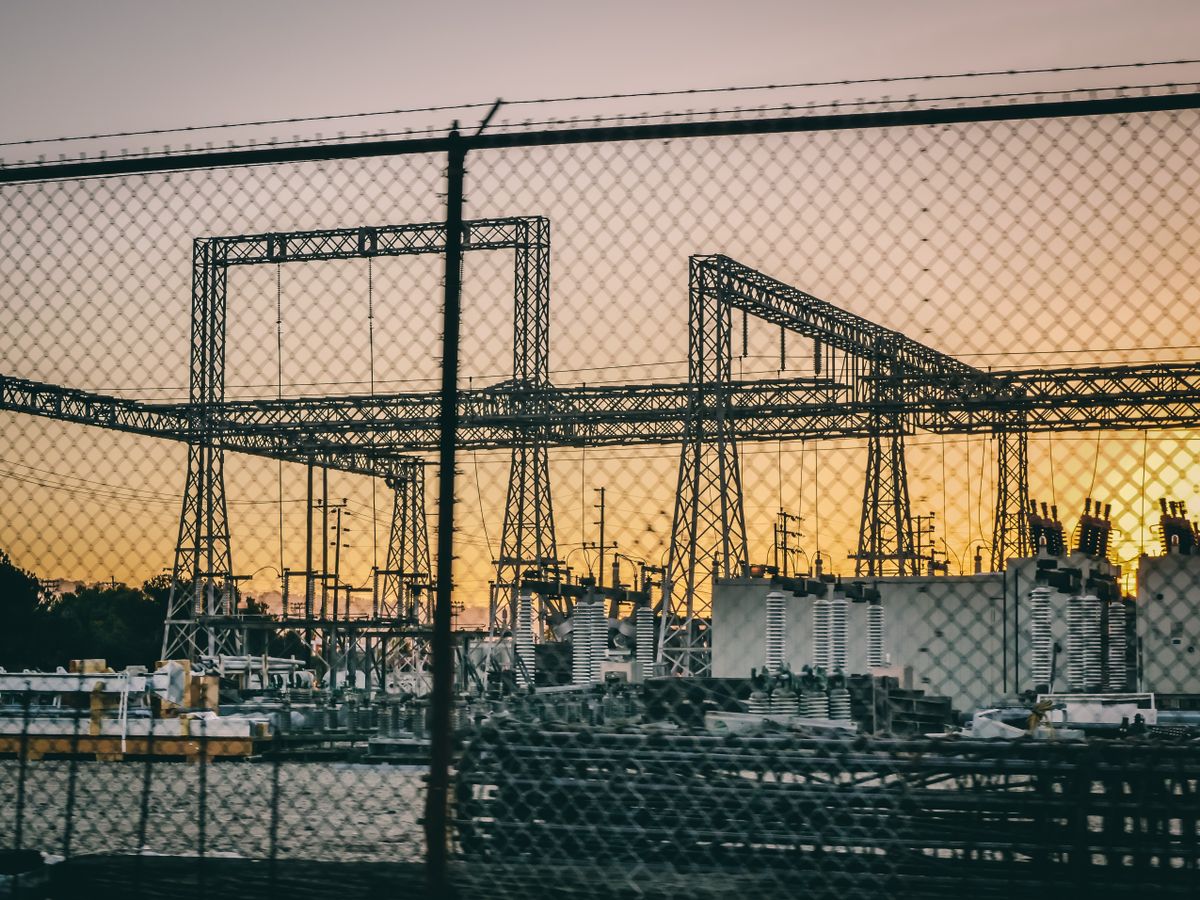
OT/ICS security for critical infrastructure
Substations, water networks, manufacturing lines and energy assets cannot be patched on a Tuesday afternoon. OT/ICS security is designed around availability first, with passive monitoring that does not disturb the process.
Passive asset discovery
Understanding controller inventories without touching production traffic.
Protocol-aware detection
Rules written for industrial protocols, not repurposed from IT logs.
Remote access control
Time-bound, supervised vendor access with full session recording.
Safety-aware response
Containment playbooks approved by engineering before they are automated.
Assurance, audit and board reporting
Security evidence is produced continuously, so regulatory audits become a retrieval exercise rather than a six-week project.
Regulatory and standards alignment
| Framework | Scope | Evidence produced |
|---|---|---|
| NERC-CIP | Bulk power system assets | Control logs, access records, audit packs |
| IEC 62443 | Industrial automation & control | Zone/conduit model, control assessments |
| ISO 27001 | Information security management | Risk register, incident and change records |
| Zero Trust | Identity, devices, network, data | Access decisions and privilege reviews |
Board risk dashboard
Resilience metrics, open exceptions and remediation ageing presented in the monthly governance cycle.
Responsible disclosure
A published path for researchers to report a vulnerability safely, with defined acknowledgement expectations.
Report a vulnerabilityStart with an exposure assessment
A four-week discovery engagement maps your IT and OT assets, ranks the gaps and returns a costed remediation sequence.
